The human firewall is not a firewall
Phishing and fiction: The human is not the control Introduction At a recent on-line presentation, we introduced the audience to a new colleague. The colleague
Phishing and fiction: The human is not the control Introduction At a recent on-line presentation, we introduced the audience to a new colleague. The colleague
Hugging Face: Over the router, through the firewall, off to Grandma’s house we go* Introduction An AI was set an exam but the exam was
Five multi-billion-dollar companies in two months… the past and the future Your Content Security Policy is strict. Your HTTP monitoring is solid. You’ve patched your
Managed SIEM services case study: tailored Splunk Enterprise Security for an Australian financial services platform A large Australian consumer-facing financial services business asked us to

Surprise PCI compliance request? An Australian SAQ guide First, don’t worry. Receiving a validation and reporting request from your payment provider is not a sign
Anthropic Mythos: The model, the myth and the mundane Anthropic Mythos (and AI in general) does pose a cyber risk! But the context and caveats
Your developers work for cyber gangs Well, not deliberately. But if they’re building software with open-source components, there’s a chance that what they shipped last
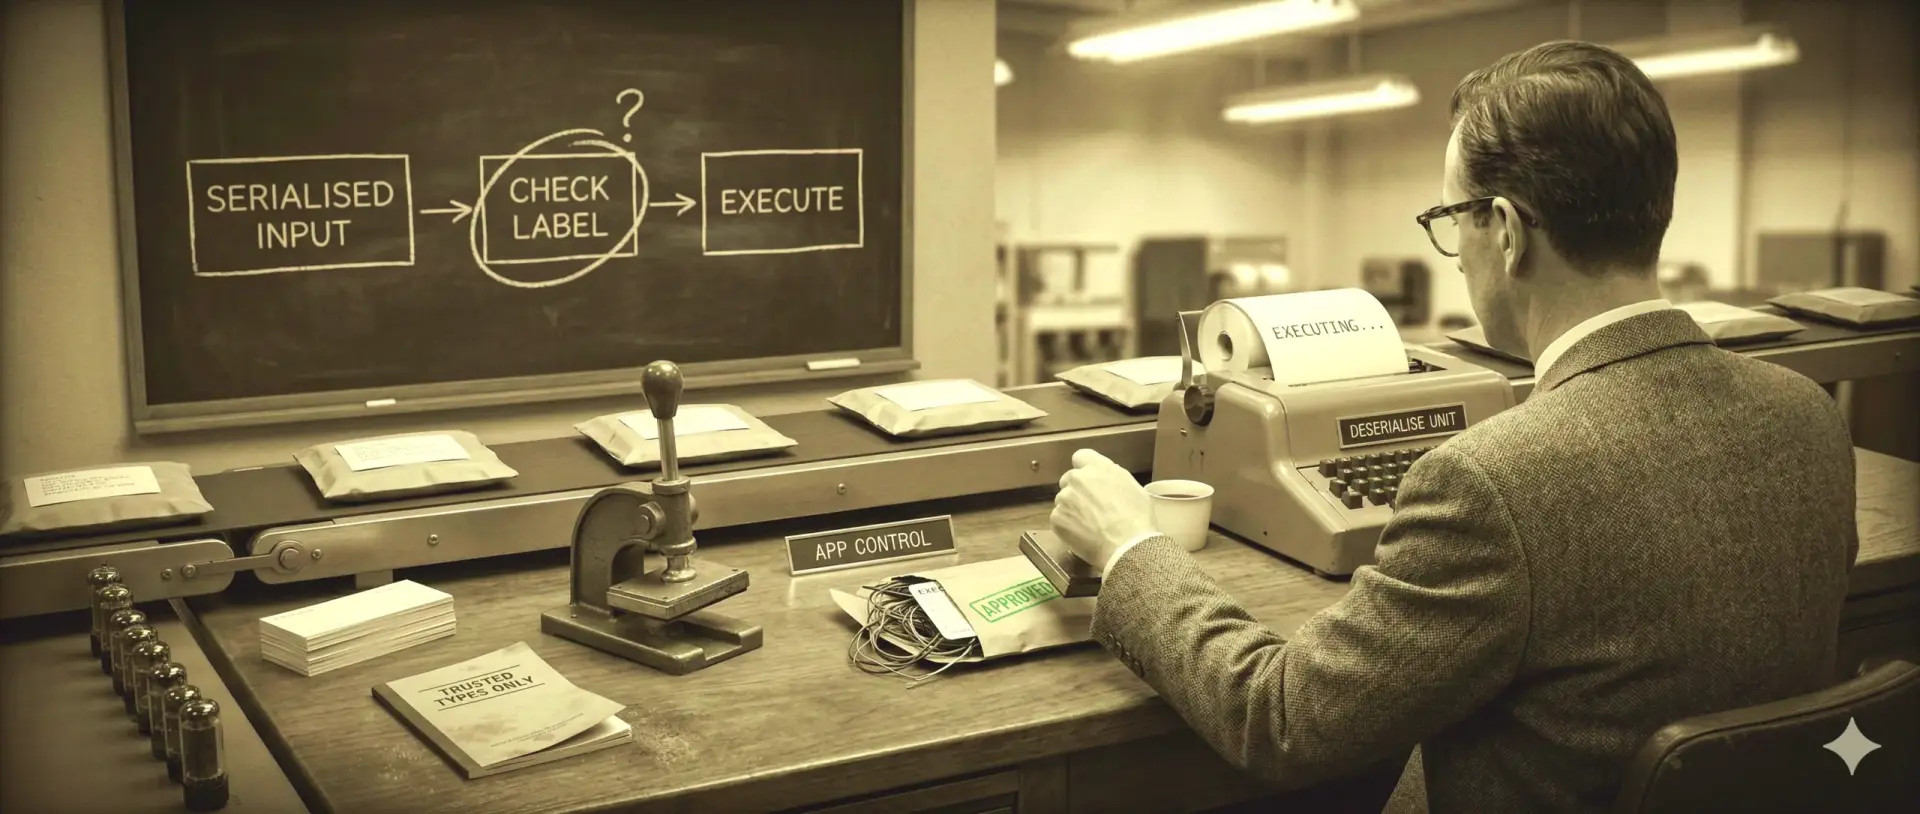
Bypassing Windows application whitelisting Application Control (formerly known as WDAC) is a native application whitelisting solution for Windows. In this post, we examine how an
MSP security – The devil’s in the detail Part two of 2-part advisory, for any Australian business that accepts card payments through a website, booking

Your MSP handles the payments but are you accepting the risk? If your website provider told you not to worry about PCI DSS because “we
FIIG FINED: Federal court orders $2.5M penalty for cyber security failures On the 9th of February 2026, the Federal Court ordered FIIG to pay $2.5

Why ransomware victims pay, and what smart organisations do instead The economics of extortion Today It’s happening all the time! In just the last six