Anthropic Mythos: The model, the myth and the mundane
Anthropic Mythos: The model, the myth and the mundane Anthropic Mythos (and AI in general) does pose a cyber risk! But the context and caveats surrounding that statement tend to get lost in mainstream media coverage. Context and caveats don’t make for apocalyptic headlines, so they get dropped… Let’s look at Anthropic Mythos: The model, […]
Bypassing Windows application whitelisting
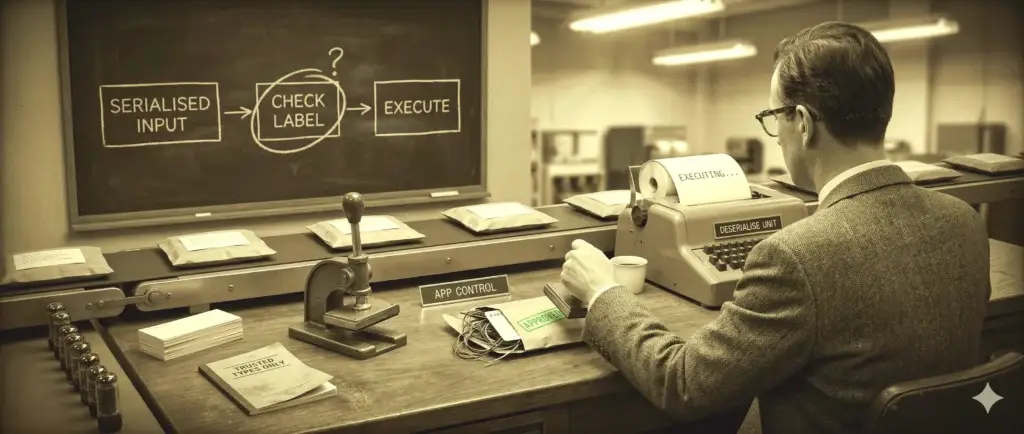
Bypassing Windows application whitelisting This post describes how we discovered and reported to Microsoft an insecure deserialisation vulnerability in one of the binaries in the Windows Assessment and Deployment Kit (ADK), and how that can be used to bypass Application Control (native Windows application whitelisting). Application Control (formerly known as WDAC) is a native application […]
Why your staff click spelling-mistake laden emails (and how to actually stop them)
Why your staff click spelling mistake-laden emails (and how to actually stop them) You have done everything “right” by the book… “Cyber Awareness” training modules… posters in the lunchroom… even warning emails about the latest package-delivery scams. Yet, when the phishing simulation results come back (or worse, when a real incident report lands on your desk […]
Proxied Execution via Custom Trace Listeners
Proxied Execution via Custom Trace Listeners Introduction to the .NET Framework and diagnostics The .NET Framework offers the System.Diagnostics.Trace and System.Diagnostics.Debug classes to help with debugging or monitoring application behaviour either during development or in Production. From the relevant Microsoft documentation: The Trace and Debug classes are identical, except that procedures and functions of the […]
DLL sideloading – Part 1
DLL Side loading – Part 1 This blog post is a result of our investigation into the process that attackers use when sideloading malicious DLLs into .NET executables. We’ll describe how and under what circumstances an attacker can get a malicious .NET DLL to be loaded by a trusted (signed) .NET executable, and we’ll also […]
Abusing Internet shortcuts for access and persistence
Abusing Internet shortcuts for access and persistence We’ve posted an update to this blog post, which we first wrote in 2025. In June 2025, Microsoft assigned CVE-2025-33053 (CVSS 8.8) to the .url file WorkingDirectory technique described in this post. The vulnerability was discovered being actively exploited by the Stealth Falcon (FruityArmor) APT group against government […]
SharpC2 in the real world
Sharpc2 in the real world SharpC2 is an open-source (.NET based) command-and-control framework developed by RastaMouse. The main component of SharpC2 is the TeamServer (and related .NET rich client) which is responsible for both generating implants (called drones in SharpC2 parlance) as well as communicating with said implants […]
DotSec’s AOC saves you money!
DotSec’s AOC saves you money! PCI DSS compliance DotSec is a PCI DSS compliant service provider and we’ll use this blog post to look specifically at what service providers need to know to operate within the context of the PCI DSS. And even if PCI DSS is not relevant to you, you might like to […]
Happy memories of an old hack
The good old (Internet banking Hack) days! So a long time ago (25 years ago actually!) in a research centre not so far away, I helped to write a paper that described an old Internet banking hack, outlined how the authentication systems that were used by browser-based internet banking applications […]
Penetration testing over two years
Case study: Penetration testing over two years It was the great Gordon Ramsay that said, “I don’t like looking back. I’m always constantly looking forward. I’m not the one to sort of sit and cry over spilt milk. I’m too busy looking for the next cow.” But still, it can’t hurt to keep track of […]