ASIC has commenced a law suit in the Federal Court of Australia. ASIC alleges [that] from March 2019 to 8 June 2023, FIIG Securities Limited failed to take the appropriate steps, as is required by an Australian Financial Services (AFS) licensee, to ensure it had adequate cyber risk management systems in place.
The filing claims that FIIG was responsible for “systemic and prolonged cybersecurity failures” that allowed attackers to exfiltrate a claimed 385GB of data, in an attack that took place at FIIG in May 2023. ASIC’s federal court application is made under sections 1101B, 1317E and 1317G of the Corporations Act 2001 (Cth) (Corporations Act).
According to ASIC, “FIIG advised ASIC that it was contacted by the Australian Signals Directorate’s Australian Cyber Security Centre (ASD’s ACSC) about a potential cybersecurity incident on 2 June 2023. FIIG was not aware the incident occurred before this contact [by the ACSC].”
Furthermore, according to ASIC, “FIIG did not investigate and respond to the incident until 8 June 2023, almost a week after it had been notified of potential malicious activity by the ASD’s ACSC.”
Leaving ALPHV free to roam about for six days is probably not going to end well, and ALPHV posted their ransom note on June 10:
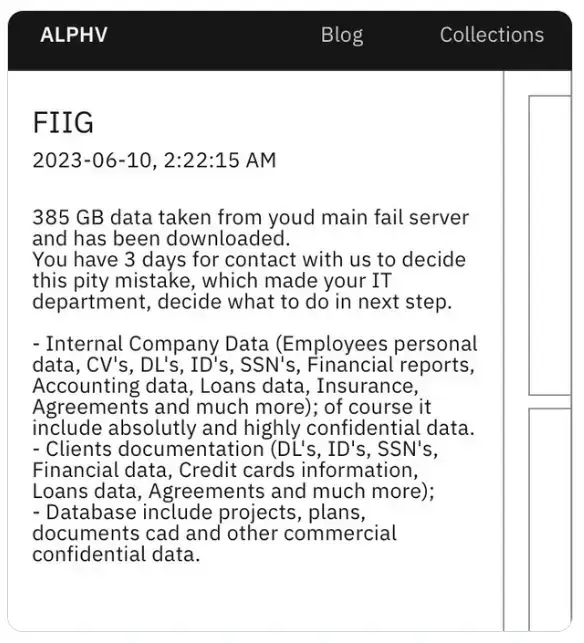
As you may remember, ALPHV was busy in 2023, having previously exfiltrated roughly 4TB of data (about 2.2 million files) as part of their breach of the law firm HWL Ebsworth (that one is apparently being investigated by the OAIC) in April of that same year.
The ASIC application states in part, that in order to meet its obligations under s 912A(1)(d), FIIG was required to have available adequate financial, technological and human resources. ASIC further states that those resources were either not available and/or ineffective, and ASIC’s notice includes a list of “Missing Cybersecurity Measures”. The list includes:
You can read more about these things… risk-management, and control frameworks, and regular testing and assessment, and AOCs in previous posts.
Two of the Missing Cybersecurity Measures that stood out for us were these:
As anyone who reads our posts (yes, both of you!) will know, we’re big on SIEM. How big? Welll…..
Why do we rabbit on about SIEM so much? Because it works and without it, you’re fighting blind! dotSec has been providing MSIEM services, assisting organizations across various industries in handling real-world cybersecurity incidents for ages. And our next post, we’ll share a presentation that we used to highlight four case studies where we’ve used SIEM to help our clients with the following:
ASIC is suing FIIG because “FIIG’s conduct exposed FIIG and its clients to the risk of a cyber intrusion and the adverse consequences thereof to a heightened and unreasonable extent”.
ASIC Chair Joe Longo stated the obvious when said, “Cybersecurity isn’t a set and forget matter. All companies need to proactively and regularly check the adequacy of their cybersecurity measures.”
As business owners, one of our jobs is to manage business risks, especially risks to our clients and staff, as well as risks associated with business continuity and integrity.
And as we know, risks can be:
We have long suggested that it is better for a business to take the initiative and spend it’s hard-earned coin on it’s own terms, managing cost and risk as part of a mature security-control and risk-management framework. The alternative approach is to have the costs and payment plan dictated by one or more third parties, whether that be an attacker like ALPHV, and/or a regulator like ASIC.
As ASIC noted in the Concise Statement, “Had FIIG had the Missing Cybersecurity Measures in place, it would have detected suspicious activity on its network on or shortly after 19 May 2023, identified that its system had been compromised by on or about 23 May 2023, and prevented the threat actor from downloading some or all of the stolen data or, alternatively, had the opportunity to do so.”
So, what happens next? Well, RI Advice incured costs of $750K in 2022, plus the “costs of Security in Depth and the implementation of any Further Measures“, with the “engagement of Security in Depth referred to in paragraph 3(a) is to commence by no later than 1 month from the date of these Orders“. According to Allens, that was apparently the first time ASIC has exercised its powers in relation to cybersecurity risk management.
I have no idea if the RI Advice case is relevant to or sets a precedent for the FIIG proceedings because this is a cyber security post, not legal advice. But if we look at the scale of the RI Advice and FIIG breaches, we see that although RI Advice suffered nine breaches over seven years, the broadest impact was described as “the potential compromise of Personal Information of several thousand clients and other persons“. “Several thousand” contrasts sharply with ASIC’s allegation that FIIG’s failings “enabled the theft of approximately 385GB of confidential data, with some 18,000 clients notified that their personal information may have been compromised“. Time will tell on that one, but the initiative does now seem to be with ASIC and the Federal Court.
As Robert S. Mueller, III, former Director of the FBI and Special Counsel into the Russian interference of the USA election noted: “There are only two types of companies: Those that have been hacked and those that will be hacked.” But Mueller’s advice was not given so that we could all just throw our hands up in the air and give ourselves over to abject, pre-ordained hopelessness like Marvin.
Meuller’s advice was in fact optimistic: It is reasonable, prudent and cost-effective to manage risk pro-actively, and to maintain a suitable level of cyber security maturity; that way, when an attack does come, there is a realistic expectation of timely detection, investigation, defence and recovery, without major consequences for the organisation’s client base.
Mueller’s advice was not only optimistic, it was also amazingly prescient in light of HWLE, RI Advice, Optus, Medibank, FIIG and so many other breaches. Why? Because Mueller made his observation in 2012!
Give us a call! We really can help with all of this and we have 25 years of references to back us up. We look forward to hearing from you soon.